Introducing Agent Runtime Security: Observe, Enforce, Audit
Which agents are running? Should this particular action be allowed? What happened, and why? This is what Arcjet is now tackling.
Arcjet Signals are evaluated without a CAPTCHA and enforced when the request passes through a critical flow. The browser gives us signals. The application gives us intent.
Arcjet Guards runs security rules inside agent tool handlers, queue consumers, and workflow steps - where proxies and WAFs can't see.
Introducing Arcjet prompt injection detection. Catch hostile instructions before inference. Works with Next.js, Node.js, Flask, FastAPI, and any JavaScript / TypeScript or Python application.
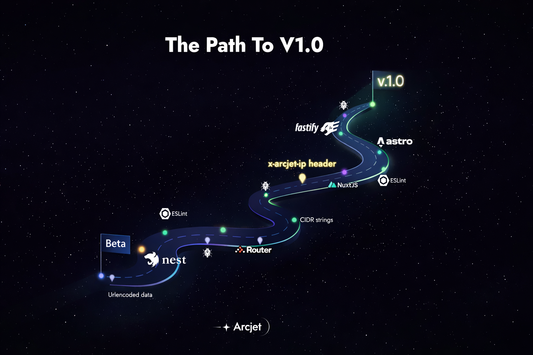
We’ve just released v1.0 of the Arcjet JavaScript SDK. After more than two years of building, testing, and iterating in public, the
The Arcjet Python SDK allows you to implement rate limiting, bot detection, email validation, and signup spam prevention in FastAPI and Flask style applications.
Get the full posts by email every week.